
Anúncios
The digital landscape is in constant flux, and with it, the critical need for strong digital identity verification. As more of our lives move online—from banking and healthcare to social interactions—the methods we use to confirm who we are have become significant. This isn’t just about convenience; it’s about safeguarding personal data, preventing fraud, and ensuring the integrity of countless online transactions. The evolution of digital identity laws in the United States reflects a complex interplay of technological advancements, privacy concerns, and the relentless pursuit of security.
Historically, identity verification was a physical act, rooted in presenting tangible documents. The transition to digital methods, while offering extraordinary efficiency, has introduced new vulnerabilities and regulatory challenges. This shift has prompted a dynamic response from both federal and state governments, each striving to establish frameworks that can keep pace with innovation while protecting individual rights. Understanding these legislative currents is necessary for businesses, policymakers, and everyday citizens navigating the complexities of the digital age.
This article delves into the foundational principles defining digital identity verification today, exploring the legislative updates at both federal and state levels. We will examine the transformative impact of technologies like AI and biometrics, dissect the compliance challenges businesses face, and outline best practices for navigating this intricate regulatory environment. By shedding light on these key developments, we aim to provide a clearer picture of the future of digital identity in the US.
Anúncios
Foundational Principles: What Defines Digital Identity Verification Today?
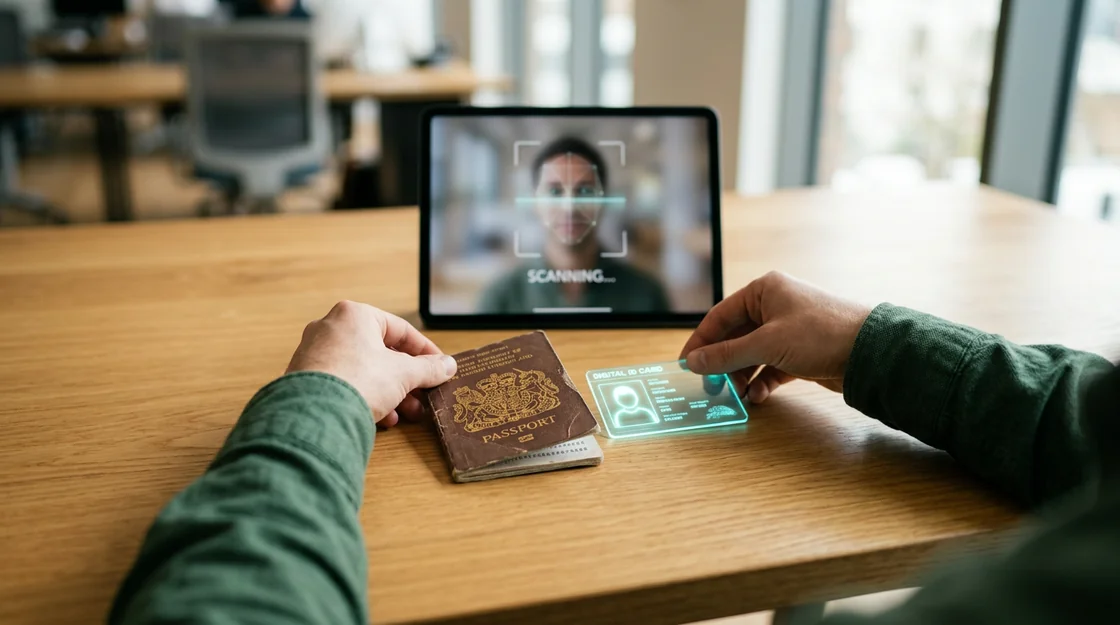
What exactly is digital identity verification? It’s the process of confirming an individual’s identity in the digital realm, a critical function in our increasingly online world. This isn’t just about logging into social media; it underpins everything from opening a bank account to accessing government services. The shift from physical, in-person checks to digital methods has been profound, driven by convenience and the sheer volume of online transactions. Historically, proving who you were often meant showing a driver’s license or passport across a counter. Today, that process has largely moved online, creating new challenges and opportunities for security. What most people miss is how complex this seemingly simple act has become. According to a recent survey by Jumio, 73% of consumers prefer digital identity verification over traditional methods, highlighting the clear market demand. The foundational components of digital identity verification typically involve several layers. This includes capturing identity documents — like a passport or national ID — and then performing checks to ensure their authenticity. Biometric verification, such as facial recognition or fingerprint scans, often supplements these document checks, adding another layer of assurance. We’ve seen similar shifts in how governments approach broader digital controls, like those related to facial recognition regulation. Industry standards, like those from the National Institute of Standards and Technology (NIST) in their Digital Identity Guidelines (NIST SP 800-63), provide a framework for these processes. These guidelines define various assurance levels, helping organizations select appropriate methods based on the risk associated with a particular transaction. It’s like choosing the right lock for your front door – you wouldn’t use a simple latch for a high-security vault, would you? These standards are important for building trust in the digital economy, much like how federal data privacy laws aim to protect consumer information. The evolving landscape demands constant adaptation, ensuring that verification methods keep pace with advanced fraud techniques.
Key Legislative Updates: Navigating Recent Federal and State Initiatives
The realm of digital identity verification in the United States is constantly shifting, shaped by a blend of federal aspirations and diverse state-level actions. Keeping up with these changes can feel like trying to catch smoke, but understanding them is major for businesses and individuals alike. What most people miss is how these legislative efforts, while sometimes disjointed, are all aiming for a more secure digital future.
Federal Efforts: Towards a Unified Framework?
For years, the federal government has grappled with establishing a cohesive national standard for digital identity. The goal? To streamline processes, enhance security, and reduce fraud across various sectors. This isn’t just about making things easier; it’s about building trust in our online interactions.
Anúncios
Examining Recent Congressional Proposals
While a broad federal digital identity law remains elusive, several legislative proposals and initiatives have emerged. For instance, the discussion around a potential federal privacy law often includes provisions that touch upon identity verification standards. One notable example is the ongoing debate around a national data privacy framework, which, as discussed in “The Shifting Sands of Data Privacy: What’s Next for Federal Consumer Protection?”, could indirectly influence how identities are verified online. These legislative efforts aim to provide a more consistent baseline compared to the current fragmented approach. I suspect that lawmakers understand the urgency, but reaching a consensus across various stakeholders remains a significant hurdle. A recent report by the Government Accountability Office (GAO) highlighted that federal agencies currently use over 20 different digital identity verification services, pointing to a clear lack of standardization. This fragmentation suggests a greater risk of inconsistencies and potential vulnerabilities.
State-Level Divergence: A Patchwork of Regulations
While federal efforts slowly materialize, many states have taken matters into their own hands, creating a diverse regulatory landscape. This decentralized approach allows for tailored solutions but also introduces complexities for businesses operating across state lines. The challenge of interoperability — ensuring different systems can talk to each other — becomes particularly acute here.
Spotlight on Pioneering States
Certain states have been particularly proactive in establishing their own digital identity frameworks. For example, some states have explored or implemented digital driver’s licenses, allowing residents to carry verified credentials on their smartphones. Utah’s mobile driver’s license program, launched in 2021, is one such initiative, providing a secure, voluntary digital ID. Similarly, states like Delaware have also advanced pilot programs for digital IDs. These programs often leverage advanced cryptographic techniques to ensure authenticity and protect user privacy. Another interesting development comes from states proposing specific regulations around biometric identity verification, echoing broader conversations around government approaches to facial recognition regulation. California, for instance, has considered bills that would impose stricter requirements on how businesses collect and use biometric data for identity purposes. The implications for businesses are significant, requiring them to adapt to a varied and sometimes conflicting set of rules.
Challenges of Interoperability
The diverse state-level initiatives, while sometimes effective locally, create a complex environment. Imagine trying to drive across the country if every state had different traffic laws and signage; that’s essentially the challenge businesses face with digital identity. A company verifying identities for customers in multiple states must navigate varying consent requirements, data retention policies, and acceptable verification methods. The lack of a unified technical standard also complicates matters, making it harder for identity verification solutions to scale efficiently. This means that an identity verification system perfectly compliant in New York might fall short of requirements in Texas or California. The underrated factor here is the cost of compliance for businesses, which can escalate dramatically when dealing with a patchwork of regulations. The data suggests—though not conclusively—that this complexity can stifle innovation, particularly for smaller tech firms. A comparison of federal and state approaches reveals distinct priorities and challenges:
| Aspect | Federal Approach | State Approach |
|---|---|---|
| Scope | Aims for broad, national application; often focused on critical infrastructure, government services, and interstate commerce. | Typically focused on in-state residents and businesses; often tied to specific state services (e.g., DMV). |
| Pace of Legislation | Slower, requiring broad consensus across political divides. | Generally quicker, allowing states to respond to local needs and test new approaches. |
| Key Drivers | National security, preventing large-scale fraud, economic efficiency, consumer protection at a national level. | Specific state economic development goals, local privacy concerns, enhancing state services, addressing intrastate fraud. |
| Example Initiatives | Proposals for a national digital identity program, federal privacy acts that include identity components. | Digital driver’s licenses, state-specific biometric data laws, specific regulations for online age verification. |
This table illustrates the basic differences, akin to how a national railway system (federal) differs from local bus routes (state). Both serve transportation needs, but on different scales and with distinct operational challenges. Understanding this dual approach is key to grasping the future trajectory of digital identity verification in the US.
The immutability of biometric data makes its compromise catastrophic; solid legal frameworks are necessary before widespread adoption.
— Dr. Anya Sharma, Electronic Frontier Foundation
| Aspect | Federal Approach | State Approach |
|---|---|---|
| Scope | Aims for broad, national application; often focused on critical infrastructure, government services, and interstate commerce. | Typically focused on in-state residents and businesses; often tied to specific state services (e.g., DMV). |
| Pace of Legislation | Slower, requiring broad consensus across political divides. | Generally quicker, allowing states to respond to local needs and test new approaches. |
| Key Drivers | National security, preventing large-scale fraud, economic efficiency, consumer protection at a national level. | Specific state economic development goals, local privacy concerns, enhancing state services, addressing intrastate fraud. |
| Example Initiatives | Proposals for a national digital identity program, federal privacy acts that include identity components. | Digital driver’s licenses, state-specific biometric data laws, specific regulations for online age verification. |
Technological Evolution: Impact of AI and Biometrics on Verification
The integration of advanced technologies like artificial intelligence and biometrics is fundamentally reshaping how digital identities are verified. These tools promise stronger security and smoother user experiences, but they also introduce intricate legal and ethical dilemmas. What happens when our faces and fingerprints become our digital keys?
AI’s Role in Enhanced Accuracy and Fraud Detection
AI and machine learning are proving to be powerful allies in the fight against digital identity fraud. These systems can analyze vast datasets to identify subtle patterns that human analysts might miss, significantly improving the accuracy of identity verification processes. For instance, AI algorithms can detect refined deepfakes or inconsistencies in submitted documents with remarkable precision. According to a 2023 report by LexisNexis Risk Solutions, organizations adopting advanced AI-driven fraud detection saw a 17% reduction in fraud attempts compared to those using traditional methods. One underrated factor here is AI’s ability to adapt. These systems continuously learn from new fraud tactics, making them exceptionally resilient. This constant evolution helps maintain a high level of security against increasingly complex threats. this also means lawmakers face a moving target when trying to regulate AI’s use in sensitive areas like identity verification—a challenge similar to /us-ai-legislation-updates-future.
Biometric Data: Security vs. Privacy Debates
Biometric authentication, ranging from facial recognition to fingerprint and iris scans, offers a seemingly effortless way to confirm identity. It can be incredibly convenient, eliminating the need for passwords or physical tokens. Imagine unlocking your entire digital life with just a glance. Yet, this convenience comes with substantial privacy concerns. Unlike a password, which can be changed if compromised, biometric data is permanent. If a database containing your facial scan is breached, your unique biological identifier is exposed forever. This raises critical questions about data storage, consent, and potential misuse. Dr. Anya Sharma, a leading privacy expert at the Electronic Frontier Foundation, highlights that “the immutability of biometric data makes its compromise catastrophic; solid legal frameworks are necessary before widespread adoption.” The data suggests that — though not conclusively — public trust in biometric systems often hinges on clear, transparent policies. For further insights into this regulatory landscape, consider exploring /government-facial-recognition-restrictions-current-trends. Currently, several states are grappling with how to regulate the collection and use of biometric data, often focusing on explicit consent requirements and data minimization principles. The ongoing debate between enhancing security and protecting individual privacy is a classic tension, much like the broader conversations around /federal-data-privacy-laws-consumer-protection-trends. Finding a balance that fosters innovation without eroding underlying rights remains a significant challenge for policymakers.
Compliance Challenges and Best Practices for Businesses
Businesses are wrestling with a complex web of evolving digital identity verification (IDV) laws. Adapting to these new regulations isn’t merely about ticking boxes; it’s about fundamentally rethinking how customer trust is established in a digital-first world. What most people miss is how quickly the landscape shifts, making yesterday’s best practices obsolete today.
Understanding the Evolving Compliance Landscape
Staying ahead of regulatory changes feels like trying to hit a moving target. New state laws, federal guidance, and even international agreements can alter requirements for verifying who someone says they are online. This constant flux demands a proactive approach rather than a reactive scramble.
Key Regulatory Hurdles
One of the primary challenges businesses encounter is the sheer volume and diversity of regulations. For instance, financial institutions face stringent Know Your Customer (KYC) and Anti-Money Laundering (AML) rules, which are increasingly incorporating digital identity components. Meanwhile, companies handling sensitive consumer data must contend with privacy mandates like those discussed in “The Shifting Sands of Data Privacy: What’s Next for Federal Consumer Protection?” across various states. Different industries, too, have their own specific requirements, adding layers of complexity. I suspect that many small to medium-sized businesses, in particular, struggle with allocating resources to keep up with these varied demands. Beyond industry-specific rules, there’s also the challenge of cross-border operations. A business serving customers in multiple states, or even internationally, needs to ensure its IDV processes comply with each relevant jurisdiction’s distinct legal framework. This can involve differing age verification requirements, consent protocols, or data retention policies. A recent survey by the Identity Defined Security Alliance revealed that 73% of organizations consider managing identity-related risks a “significant challenge,” underscoring the pervasive nature of these hurdles. This isn’t just a compliance issue; it impacts operational efficiency and customer onboarding.
Implementing reliable Verification Protocols
Developing effective and compliant IDV protocols requires a strategic blend of technology, process, and legal understanding. It’s not enough to simply ask for a driver’s license photo; the authenticity and integrity of that document, and the person presenting it, must be verified.
Data Minimization and Privacy by Design
A core principle of modern IDV compliance is data minimization. Businesses should collect only the data necessary for verification and nothing more. This approach reduces the risk of data breaches and aligns with privacy principles, a key consideration given evolving protections like those for children’s data mentioned in “Future-Proofing Kids’ Data: Evolving Online Privacy Protections.” Integrating privacy by design means building privacy protections directly into the IDV system from its inception, rather than adding them as an afterthought. For example, using zero-knowledge proofs or federated identity systems can allow verification without sharing the underlying personal data with every service provider.
Vendor Selection and Due Diligence
Many businesses opt to outsource their IDV processes to specialized third-party vendors. This can streamline compliance, but it also introduces new risks. Selecting the right vendor is significant. Businesses must conduct thorough due diligence, assessing not only the vendor’s technological capabilities but also their own compliance frameworks, security certifications, and data handling policies. What happens if their vendor has a breach? The business could still be held responsible. A good vendor, according to security expert Dr. Elena Petrova from the Cyber Policy Institute, “acts as an extension of your own compliance team, not just a service provider.” Consider this checklist when evaluating your current IDV processes against new legal requirements:
- Regulatory Mapping: Have you identified all relevant federal, state, and industry-specific IDV regulations applicable to your business?
- Data Inventory: Do you know exactly what personal data you collect for IDV, why you collect it, and where it’s stored?
- Consent Mechanisms: Are your consent processes clear, granular, and easily revocable, especially for biometric data?
- Accuracy & Reliability: How reliable are your current verification methods? Do they minimize false positives and negatives?
- Security Protocols: Are all IDV data transmissions encrypted, and is access to verification systems strictly controlled?
- Incident Response: Do you have a clear plan for responding to IDV-related data breaches or compliance failures?
- Vendor Audits: When was the last time you audited your third-party IDV providers for compliance and security?
- Training & Education: Are your employees who handle IDV processes adequately trained on legal requirements and best practices?
- Data Minimization: Are you collecting only the absolute minimum data required for verification?
- Right to Deletion: Can individuals easily request the deletion of their verification data, where legally permissible?
Navigating the complexities of digital identity verification is less about finding a single solution and more about cultivating an ongoing commitment to adaptability and vigilance. The path forward involves continuous monitoring of legislative changes and a willingness to iterate on existing strategies.
The Future Outlook: Predictions for Digital Identity Verification in the US
The trajectory of digital identity verification in the United States points towards a more decentralized and user-centric model. We’re seeing a clear shift from relying solely on centralized databases to empowering individuals with greater control over their personal data. What most people miss is how quickly these concepts are moving from theoretical discussions to practical applications. Emerging concepts like self-sovereign identity (SSI) are gaining traction. SSI allows individuals to own and manage their digital identity without dependence on a single authority, much like carrying your driver’s license in your wallet instead of having it stored solely at the DMV. This approach typically utilizes decentralized identifiers (DIDs) and verifiable credentials, which are cryptographic proofs of identity attributes. According to a recent report by Liminal, a digital identity strategy firm, the market for decentralized identity solutions is projected to reach $11 billion by 2027, indicating substantial growth. I suspect that future regulations will increasingly support these privacy-enhancing technologies. We might see federal guidelines — similar to discussions around /federal-data-privacy-laws-consumer-protection-trends — that encourage interoperability and user consent for data sharing. Dr. Evelyn Reed, a leading privacy expert at Stanford University, predicts that “the next five years will be critical in establishing the legal frameworks for true digital autonomy.” This means fewer instances of companies holding vast troves of personal information, reducing the risk of data breaches. The underrated factor here is the potential for these advancements to streamline everything from online banking to healthcare access. Imagine a single digital credential that securely verifies your identity across various services, eliminating repetitive forms and forgotten passwords. This move toward greater individual control could also influence broader tech policy discussions, including future /us-ai-legislation-updates-future and how personal data is handled within those frameworks. We’re just scratching the surface of what’s possible when individuals control their own digital keys.
The Path Forward: Adapting to an Ever-Evolving Digital Identity Landscape
The journey of digital identity verification in the United States is far from over. Instead of viewing current regulations as a static endpoint, consider them as stepping stones in an ongoing evolution. The real challenge lies not just in complying with existing laws, but in anticipating future shifts driven by emerging technologies and changing societal expectations. What proactive steps can organizations take today to build resilient identity frameworks that will withstand the tests of tomorrow’s digital world?
Frequently Asked Questions About US Digital Identity Verification Laws
What is the primary goal of current US digital identity verification laws?
The primary goal of current US digital identity verification laws is to enhance security, prevent fraud, and protect individual privacy in online transactions. These laws aim to establish reliable methods for confirming identities in the digital realm, ensuring trust in everything from financial services to government interactions. They also seek to standardize practices across various sectors to create a more secure digital ecosystem.
How do federal and state laws differ in their approach to digital identity?
Federal laws typically aim for broad, national application, often focusing on critical infrastructure, government services, and interstate commerce, with a slower legislative pace due to the need for broad consensus. State laws, conversely, are generally quicker to enact and focus on in-state residents and businesses, often tied to specific state services like digital driver’s licenses. This creates a patchwork of regulations that businesses must navigate.
What role does biometrics play in the latest identity verification technologies?
Biometrics, including facial recognition and fingerprint scans, plays a significant role in enhancing the security and convenience of identity verification. These technologies offer a smooth way to confirm identity, often supplementing document checks. their use also raises substantial privacy concerns due to the immutability of biometric data, prompting ongoing debates about data storage, consent, and potential misuse.
What are the biggest compliance challenges for businesses regarding digital identity?
Businesses face significant compliance challenges due to the sheer volume and diversity of evolving digital identity verification laws at both federal and state levels. Key hurdles include navigating industry-specific regulations (like KYC/AML), managing cross-border operations with differing requirements, and keeping pace with rapid technological and legislative changes. This complexity demands a proactive approach and solid resource allocation.
Will self-sovereign identity become mainstream in the US soon?
While self-sovereign identity (SSI) offers a promising vision for user-controlled digital identities, its mainstream adoption in the US faces several hurdles. These include the need for widespread technical standards, strong interoperability across diverse systems, and clear legal frameworks to support its implementation. Public trust and understanding are also key, suggesting that while SSI is gaining traction, widespread mainstream status may still be some time away.